Op-ed by Dr. Manfred Boudreaux-Dehmer
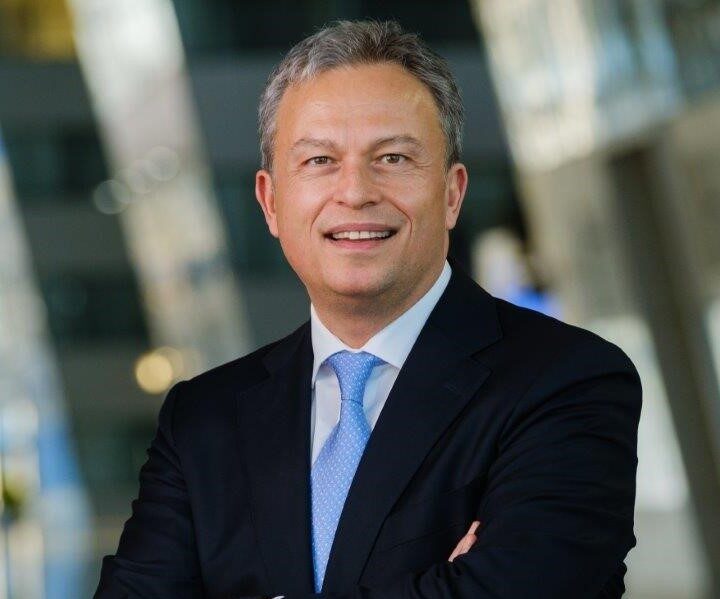
Dr. Manfred Boudreaux-Dehmer was the inaugural Chief Information Officer (CIO) and Chief Information Security Officer (CISO) of the North Atlantic Treaty Organization (NATO). He reported to NATO’s Secretary General with principal responsibility for realizing the Allies’ vision for IT in support of NATO’s purpose to safeguard freedom and security for one billion people in 32 member nations.
We are not at peace in cyberspace. One could be tempted to call it war, since our current situation tends to feel like a war, but this term is of course highly charged. It invokes von Clausewitz, the UN Charter, and the Geneva Conventions, but what we call it does not really matter that much. Perhaps one could settle on the term ‘unpeace’ – this is what my friend Dr. Lucas Kello, Co-Director of the Center for Doctoral Training in Cyber Security at Oxford University, calls it.
I believe that this is the clearest description of where nations stand in cyberspace today. The first two articles in this series examined how states bring offensive capabilities closer to the center of their cyber strategies and the risks that come with this shift. While I take those risks seriously, I also believe governments need offensive cyber capabilities to level the playing field in the fight against bad actors. These actions must be anchored in ethics and governed by effective oversight that includes robust safeguards and strong legal protections. Even under those conditions, I believe that such capabilities must remain the responsibility of governments. Companies should not become state-sponsored proxies nor take offensive capabilities into their own hands.
Most recently, I served as NATO’s Chief Information Officer and Chief Information Security Officer. As one can imagine, the North Atlantic Treaty Organization’s cyber threat picture is unique and the risks to the Alliance’s systems are substantial. In that role, I saw firsthand how the cyber threat landscape has evolved. Russia, China, North Korea, and Iran are the main state-linked actors targeting the Alliance, and they do not wait for a declaration of war. As an example, cyber incidents linked to Russia rose by 800% in the run-up to the invasion of Ukraine in February 2022. That is not what quiet peace looks like.
Against that pressure, a purely defensive posture is no longer sustainable. Defense is essential, but a defender who never imposes a cost teaches the attacker that probing is free. As things currently stand, our adversaries and competitors face few consequences for their offensive cyber actions. I firmly believe that deterrence needs both a credible threat of response and the clear ability to carry it out.
Artificial Intelligence adds urgency to this challenge because it is accelerating both offensive and defensive capabilities. AI is helping defenders detect threats and respond more quickly, but it is also making offensive capabilities faster, cheaper, more scalable, and increasingly automated. The result is a threat environment that moves at a pace few organizations or governments are prepared to match, and which requires responses and the adoption of best-in-breed technologies on a much more rapid timescale.
The challenge is not simply to keep up with technological change, but to ensure that security, accountability, and resilience keep pace with it. As cyber capabilities become increasingly automated, clear rules, effective oversight, and trusted cooperation between governments and industry become ever more important.
As previous posts in this series have examined, greater offensive activity can heighten tensions and increase the risk of miscalculation. But that risk must be weighed against the alternative and the situation we already face: persistent aggression met with an insufficient response to deter future aggression. In my view, clinging to a ‘defensive-only’ posture carries greater risk.
Even so, offensive operations must be carefully orchestrated. They should be necessary and proportionate to the threat, carried out only by authorized state institutions within strict legal and operational boundaries, and subject to meaningful oversight and accountability. Where those conditions are missing, the case for offensive capabilities weakens, and so does trust among the public and industry. Where they are in place, offensive capabilities become one tool in the national security toolkit alongside conventional military capability. Having these tools in place also provides much-needed legal clarity, since a government that can explain who authorized an operation and its legal basis is less likely to be misread by other states. The more powerful the tool, the tighter the control must be.
In contrast, private “hack back” activities – when a company retaliates against whoever it believes has attacked it – would turn cyberspace into a Wild West. A company sees only one part of the picture. By default, it cannot fully assess the consequences for national security, and it is not subject to the oversight expected of state institutions. A mistaken attribution may have consequences far beyond the companies involved. The server that appears to belong to an attacker could, for example, be part of a hospital’s hijacked infrastructure or a cloud service relied upon by hundreds of companies and government services. Once retaliation becomes a private option, the risk of escalation and collateral damage grows rapidly, and there is no clear line telling companies when to stop. That is why offensive operations should always remain a state’s responsibility.
Restraint does not mean passivity, though. Companies also have important responsibilities: to harden their systems, report incidents, share what they learn with national authorities and allies, and build the resilience and defense capabilities that keep services running under attack.
Effective cybersecurity and resilience depend on partnership. Governments and companies see different parts of the picture, bring different capabilities to the table, and have different responsibilities. The private sector operates much of the infrastructure that societies depend on, while governments retain responsibility for national security and the legitimate use of state power.
That distinction matters, and governments and the private sector play distinct, non-interchangeable roles. Companies should focus on defense, resilience, and cooperation with public authorities. Governments should conduct offensive cyber operations in a manner that is accountable, legally grounded, and firmly under state control.